ClawQLDefense in depth — every layer assumes the one before it can fail.
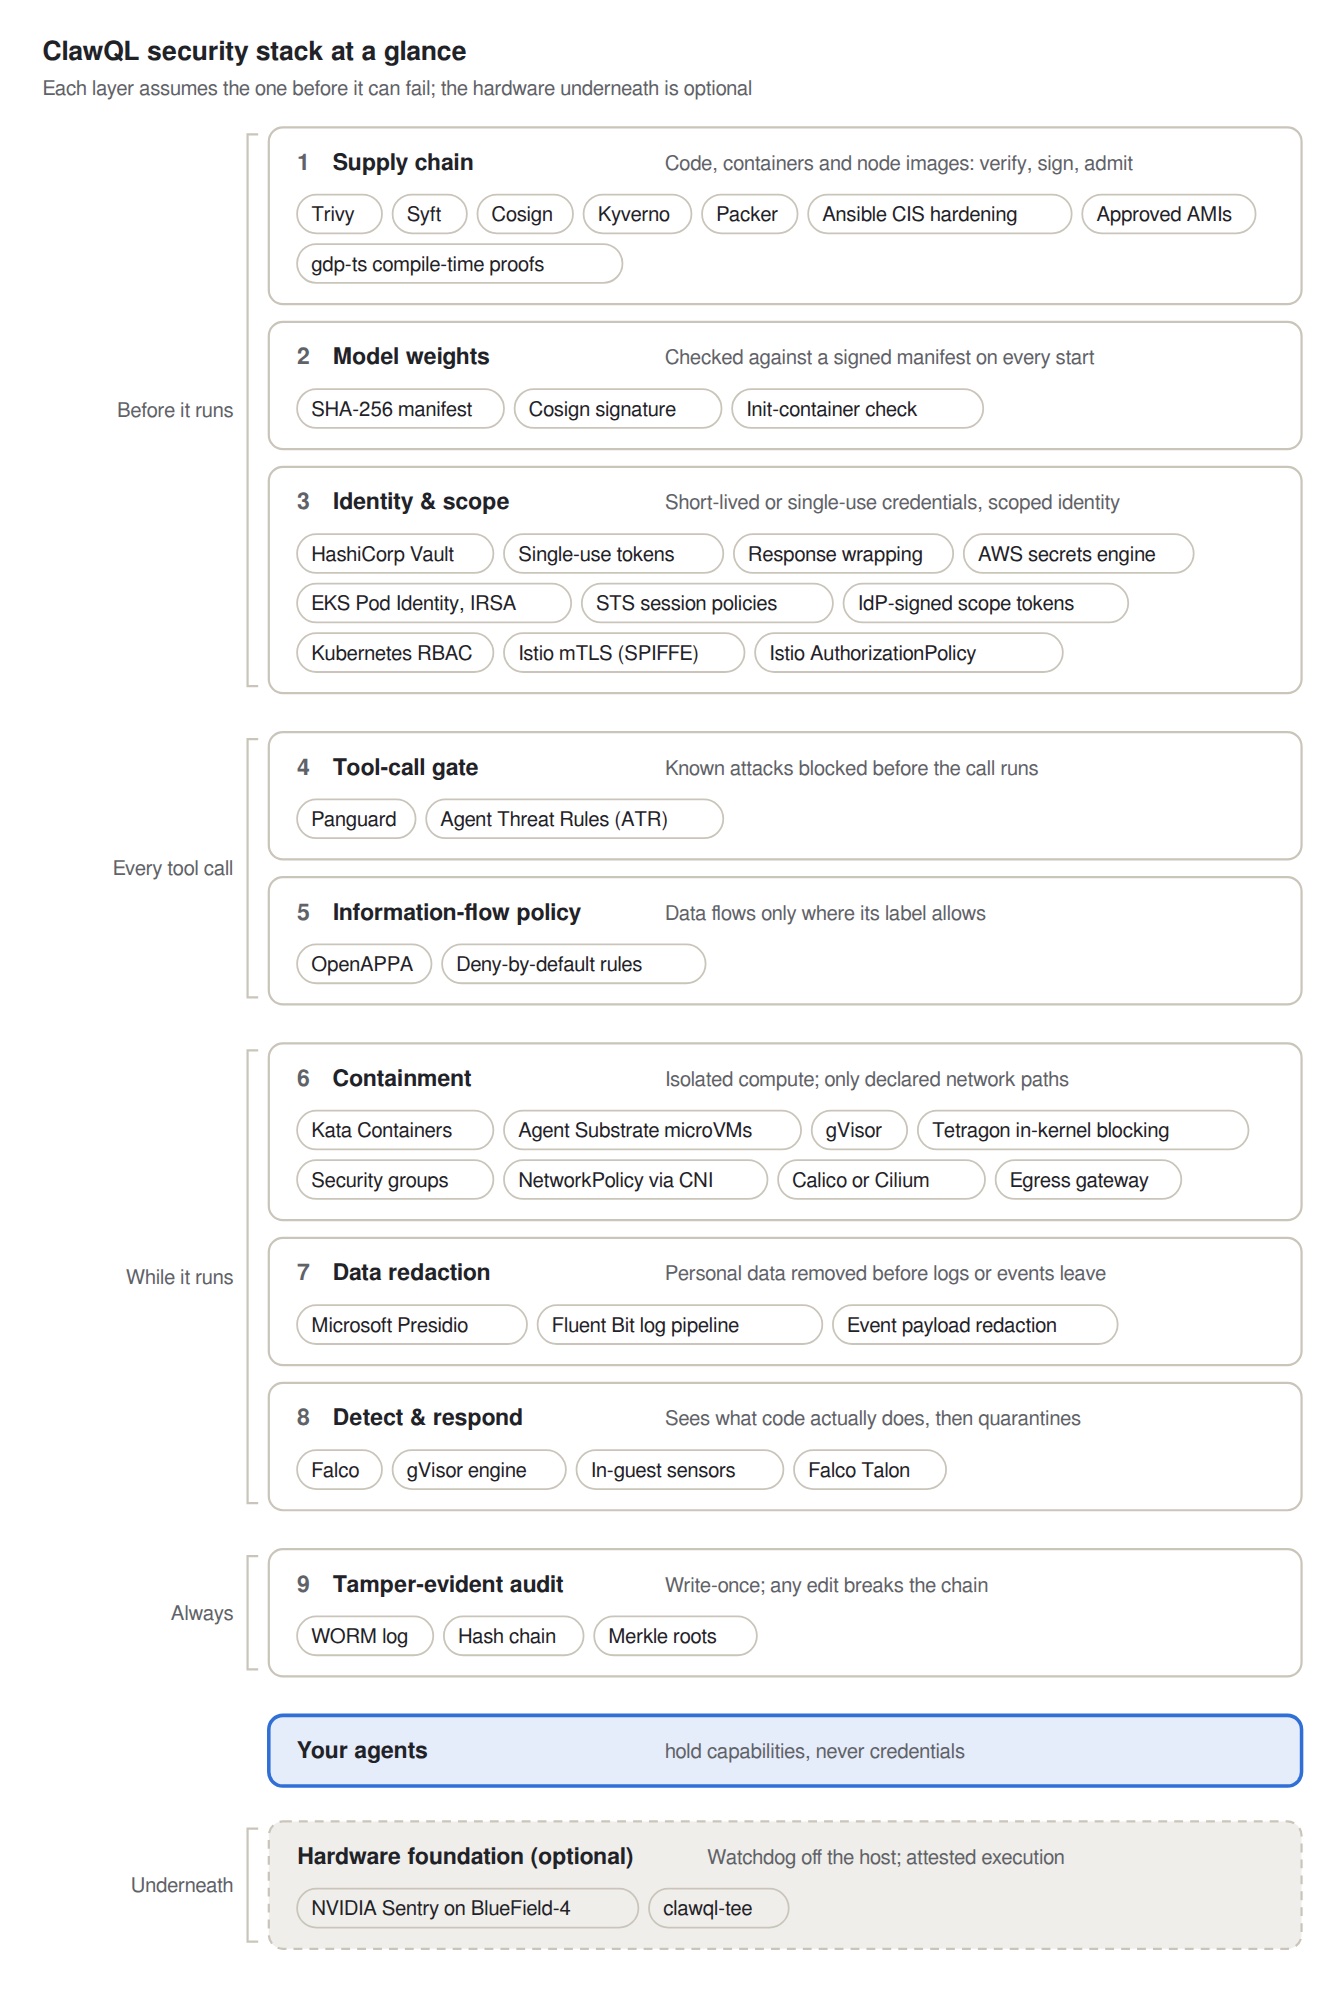
ClawQL’s security stack runs from supply chain through tool-call gates, containment, redaction, detection, and tamper-evident audit. Hardware attestation underneath is optional when the operator itself cannot be trusted.
Admit only what you can prove
Layers 1–3 in the stack.
- 01
Supply chain
Code, containers and node images: verify, sign, admit.
- Trivy
- Syft
- Cosign
- Kyverno
- Packer
- Ansible CIS hardening
- Approved AMIs
- gdp-ts compile-time proofs
- 02
Model weights
Checked against a signed manifest on every start.
- SHA-256 manifest
- Cosign signature
- Init-container check
- 03
Identity & scope
Short-lived or single-use credentials, scoped identity.
- HashiCorp Vault
- Single-use tokens
- Response wrapping
- AWS secrets engine
- EKS Pod Identity
- IRSA
- STS session policies
- IdP-signed scope tokens
- Kubernetes RBAC
- Istio mTLS (SPIFFE)
- Istio AuthorizationPolicy
Block bad calls before they run
Layers 4–5 in the stack.
- 04
Tool-call gate
Known attacks blocked before the call runs.
- Panguard
- Agent Threat Rules (ATR)
- 05
Information-flow policy
Data flows only where its label allows.
- OpenAPPA
- Deny-by-default rules
Contain, redact, and respond
Layers 6–8 in the stack.
- 06
Containment
Isolated compute; only declared network paths.
- Kata Containers
- Agent Substrate microVMs
- gVisor
- Tetragon in-kernel blocking
- Security groups
- NetworkPolicy via CNI
- Calico or Cilium
- Egress gateway
- 07
Data redaction
Personal data removed before logs or events leave.
- Microsoft Presidio
- Fluent Bit log pipeline
- Event payload redaction
- 08
Detect & respond
Sees what code actually does, then quarantines.
- Falco
- gVisor engine
- In-guest sensors
- Falco Talon
Audit that cannot be silently rewritten
Write-once; any edit breaks the chain.
- 09
Tamper-evident audit
Write-once; any edit breaks the chain.
- WORM log
- Hash chain
- Merkle roots
Your agents
hold capabilities, never credentials — scopes and ATR decide what runs, not long-lived secrets in prompts.
Hardware foundation (optional)
Watchdog off the host; attested execution.
- NVIDIA Sentry on BlueField-4
- clawql-tee
When the operator itself cannot be in the trust model, see clawql-tee for attested Durable Object–compatible execution.
Read the full security documentation
Golden-image pipelines, admission enforcement, and the agentic AI curriculum live on docs — this page is the stack map.